whoami
Giulliano Amaral
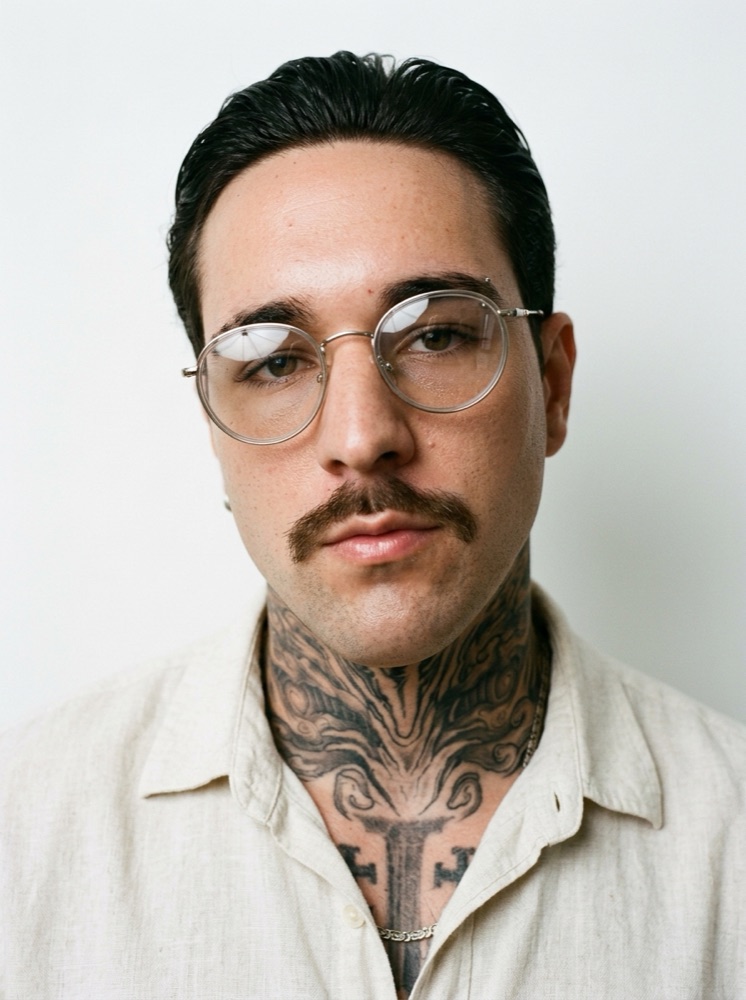
I'm a penetration tester and offensive security researcher based in Rio de Janeiro. I've worked on both sides: in a SOC, triaging alerts and responding to incidents, and as the lead of a pentest team. Having seen how attacks look from the defender's seat shapes how I test and how I write findings up.
My work focuses on web applications and APIs, Active Directoryand, increasingly, AI/LLM systems and the agents built on them. Outside client work I hunt bugs in open-source software and publish what I learn here and on YouTube.
I keep my skills sharp with CTFs: 43 HackTheBox machines and 138 TryHackMe rooms, more than 300 hours of hands-on labs. On HackTheBox I've reached the top 80 in Brazil, at the Pro Hacker rank, and I play the competitive seasons. On TryHackMe I'm in the top 2% worldwide. I also solved 6 Advanced and Expert challenges in the Arkx AI Red-Team CTF, which focuses on attacking AI agents.
I hold a postgraduate degree in Red Team operations and 7 hands-on offensive certifications. I speak Portuguese, English, Spanish and Japanese (日本語). You can reach me at giuskywalker@pm.me.
cat experience.log
Experience
Penetration testing engagements, bug bounty and open-source vulnerability research.
Led the pentest team and owned the security infrastructure.
Detection engineering, alert triage and incident response.
Network operations and monitoring.
cat ethics.md
Rules of engagement
I only test systems with written authorization from their owner. Client findings are never published. The writeups here cover retired HackTheBox machines and lab platforms; writeups for active machines are sealed. Vulnerabilities in open-source projects are disclosed only after the maintainers publish a fix.
./contact --scope yours
Have something in scope?
Tell me about the target, the environment and your timeline. I'll come back with questions and a proposed approach. Testing only starts with written authorization.